Python Network Automation: Proactive DNS Monitoring & Prevention
Proactive DNS monitoring, automated threat detection, operational visibility, and incident prevention.
Engineering Problem
Reactive DNS troubleshooting and fragmented security monitoring can leave service disruptions, configuration anomalies, and suspicious activity undetected until operational impact occurs. Manual monitoring and disconnected event records limit visibility, increase investigation time, and complicate incident response coordination. Engineering teams need continuous monitoring, centralized event analysis, and repeatable alerting workflows to identify emerging problems before they escalate into significant incidents.
Technical Solution
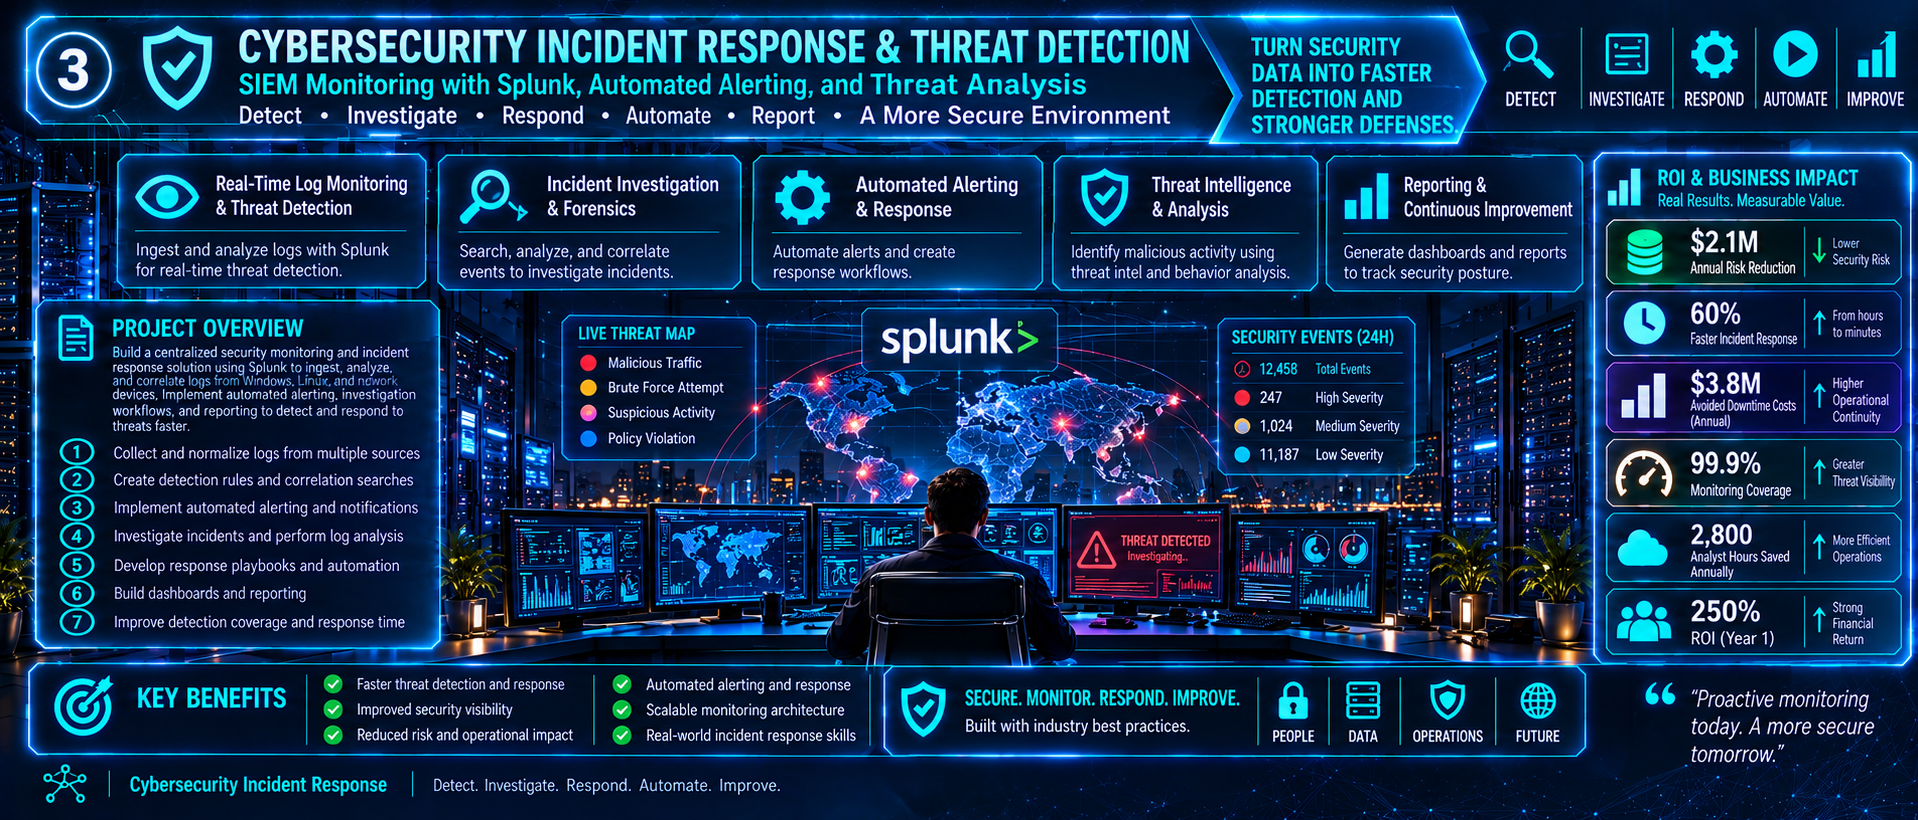
Extended Python-based DNS incident response into a proactive monitoring framework using recurring device health checks, DNS status evaluation, and structured operational reporting. Incorporated security monitoring concepts using Splunk SIEM, centralized log analysis, event correlation, and automated alerting to support threat detection and incident investigation. Organized monitoring results, security observations, dashboards, and response procedures into a repeatable workflow focused on early detection, operational visibility, and service continuity.
Business & Technical Value
Business Value:
- Reduce operational disruption through earlier identification of DNS failures, abnormal device conditions, and potential security incidents.
- Improve engineering productivity through automated monitoring, centralized reporting, and more efficient incident triage.
- Strengthen business continuity and security posture through improved threat visibility, consistent alerting, and proactive service monitoring.
Technical Value:
- Demonstrate Python automation, DNS health monitoring, recurring device checks, and structured operational data collection.
- Apply SIEM monitoring concepts, Splunk log analysis, event correlation, threat detection, and automated security alerting.
- Establish repeatable monitoring, incident investigation, dashboard reporting, and response verification workflows.
Tools & Capabilities
Core Tools:
Supporting Technologies:
Implementation & Validation Highlights
- Proactive DNS & Device Monitoring: Designed recurring Python-based monitoring workflows to evaluate DNS resolution, device connectivity, service health, and abnormal operating conditions before they escalate into outages.
- Security Event Detection & Analysis: Applied centralized logging, Splunk SIEM monitoring concepts, event correlation, and automated alerting workflows to identify suspicious activity and support structured incident investigation.
- Operational Validation & Reporting: Organized monitoring results, security observations, dashboards, and structured reports to support service verification, incident documentation, response coordination, and continuous improvement.
Return on Investment (ROI)
Explore the supporting portfolio
The canonical engineering documentation and infographics remain in the separate public portfolio repository.
Explore Project 03 on GitHub ↗